GitBook Security Incident Review, Attack Targeting Trade.xyz

 Prefer us on Google


On November 5, GitBook released a review of the security incident that occurred on November 2. The attacker exploited a vulnerability in the single sign-on process to forge employee login sessions, query improperly configured GitHub App authentication information within the organization, access internal code repositories, and obtain Cloudflare API keys, ultimately gaining full production environment permissions. GitBook disabled the relevant internal service accounts to cut off the attack within hours, resulting in the platform being offline for approximately 16 hours, and it was fully restored on November 3 at 11:56 UTC. The attacker remained in the production environment for a total of about 3 hours and 25 minutes. GitBook has rotated all infrastructure and revoked customer keys and API tokens. GitBook stated that current indications show the attack targeted a single customer rather than the entire platform, and no other customer content has been found to be tampered with. However, since the attacker had access to customer data within the platform, it has been treated as if all customer data may have been exposed, involving API tokens, integration keys, session signature keys, assistant Q&A records, and authorized repository permissions for GitHub and GitLab applications. Billing information, passwords, and IP addresses were not affected. The speed and precision of the attack heavily relied on automation and AI. SlowMist's Chief Information Security Officer 23pds forwarded the review, stating that the targeted entity was Trade.xyz. Trade.xyz indicated that the document anomaly stemmed from an intrusion into GitBook's infrastructure, and there are no signs of compromise in its own infrastructure, and it will migrate away from GitBook within a few days.
-- Price
This content is provided for general informational purposes only and doesn't constitute financial, investment, legal, or tax advice. Any events, rewards, online promotions, or related information mentioned herein should not be considered a recommendation, solicitation, or invitation to purchase, sell, trade, or otherwise deal in any crypto assets. Crypto assets are highly volatile and may result in loss. The availability of WEEX services, products, and related events may vary by region. You are responsible for ensuring that your participation is in accordance with applicable local laws and regulations.
You may also like
AI Agents Do More Than Just Place Orders: The Next Entrepreneurial Opportunity Lies in Matching and Trust
NVIDIA Scandal Shakes the Internet! How Should Cryptocurrency Be Divided After a Divorce with a Tech Tycoon?
Bundesbank President Says Economic Recovery Faster Than Expected, Structural Reforms Needed
Immutable Chain's Transition to OP Stack: What Changes for Users
Ledger CEO faces backlash after saying everybody will be hacked at some point
WEEX 11.11 Shopping Fest: Buy BTC and Unlock Up to 888 USDT in Rewards
NEAR AI Discloses SGLang Security Incident and Revokes Exposed API Keys
The Art of Trading: How They Profit from Arbitraging USDE Stocks
VARA Is Not a Panacea: Dubai's Crypto Payments Still Depend on the Central Bank
a16z Frontier Partner: Agents Should Rebuild Uber-like Transaction Networks
Poland's Parliament Votes 240-202 To Let Officials Freeze Crypto Before Court Review
WEEX P2P now supports ILS, BHD, OMR & QAR —Merchant Recruitment Now Open
Cryptocurrency Security Checklist: Four Lessons from Phemex Safety Hub Vol. 05–08
Ondo Claims $4B in Tokenized Assets as RWA Market Gains Institutional Depth
DTCC Launches Tokenization Service: What Can Investors Actually Do?
The catch in recovering a hacked crypto wallet: the thief may still have a key
Bitcoin Remains Strong: Why $76,000 is the Level That Matters Now
Peter Schiff Criticizes Strategy's Bitcoin Purchases
iPhone Attack Kit 'DarkSword' Suspected of Being Misused for Cryptocurrency Theft, Bitquery Identifies Approximately $4.06 Million in Stolen Funds
Financial and Political Crisis in Paraguay: How the Ueno Bank Explosion Triggered the President's Resignation
OpenAI Releases National Community Covenant and Computing Park Policy Blueprint
Post-Quantum Era Consensus Layer Divergence: Ethereum Maintains Decentralization, Monad Prioritizes Speed
The Ghost Behind the Screen: Unveiling the Secret World of North Korean Hackers Lazarus
Bitcoin Miners Turn to AI: Escaping the Crypto Cycle, but Entering New Turbulence
Decoding Variational: How a No-Order-Book Exchange Became the Dragon Behind Hyperliquid?
Creators Speak | The Biggest Risk in the Crypto Industry is Thinking It's Safe
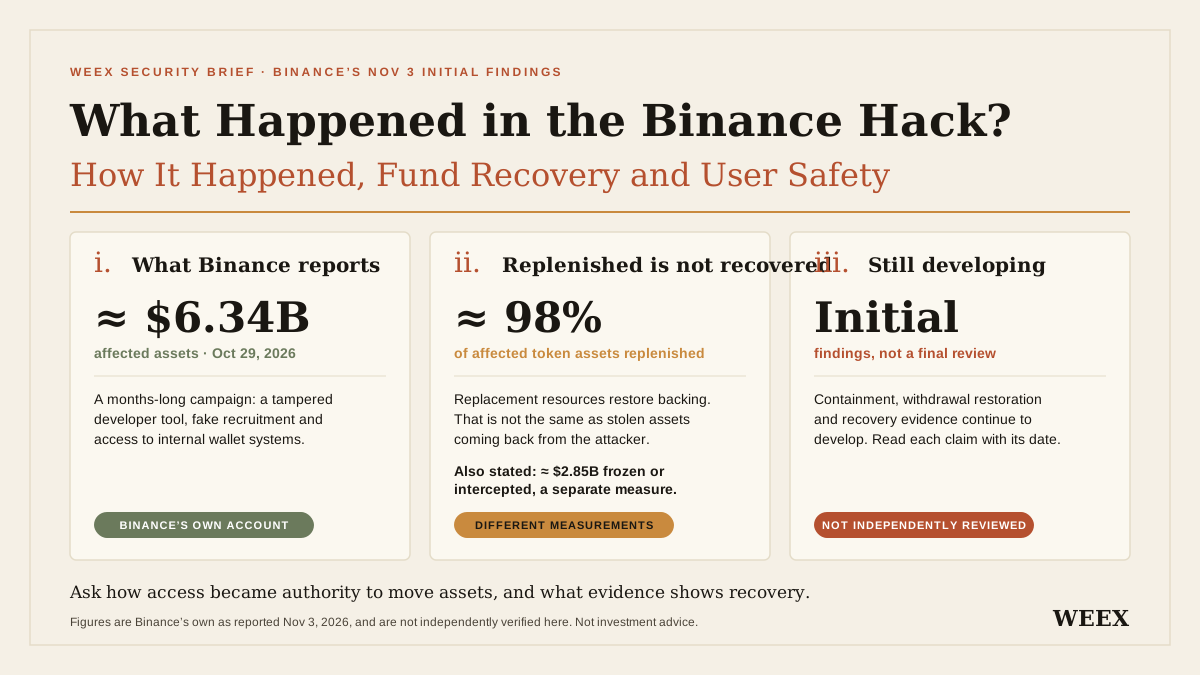
What Happened in the Binance Hack? How It Happened, Fund Recovery and User Safety
What happened in the Binance hack? Review the attack timeline, latest fund replenishment, recovery limits and practical steps to protect your account.
Who really controls a crypto project? Inside the SEC’s new guidance
Reflections After the Binance Heist: Who Should We Trust with Our Crypto Assets?
Solana study finds wider spreads outside aggregators at five of six sampled pools
AI Agents Do More Than Just Place Orders: The Next Entrepreneurial Opportunity Lies in Matching and Trust
NVIDIA Scandal Shakes the Internet! How Should Cryptocurrency Be Divided After a Divorce with a Tech Tycoon?
Bundesbank President Says Economic Recovery Faster Than Expected, Structural Reforms Needed
Immutable Chain's Transition to OP Stack: What Changes for Users
Ledger CEO faces backlash after saying everybody will be hacked at some point
WEEX 11.11 Shopping Fest: Buy BTC and Unlock Up to 888 USDT in Rewards
Latest articles




Latest coin listings on WEEX


