
Coldcard hackers leave 87% of stolen Bitcoin unmoved after $114M theft

 Prefer us on Google


More than 87% of the Bitcoin attributed to the Coldcard hack has remained unmoved, leaving 1,561 BTC under attacker control after researchers linked the exploit to $114.7 million in losses.
Summary
- Galaxy Research traced 1,789 BTC stolen from 8,865 addresses to the Coldcard hack.
- About 1,561 BTC, or 87.3% of the attributed losses, remains unmoved.
- Some Bitcoin from later attacks has moved through CoinJoin transactions and peel chains.
- Galaxy has shared identified attacker addresses with exchanges, compliance firms and law enforcement.
Galaxy Research has traced 1,789.28 BTC stolen from 8,865 addresses to the Coldcard exploit, according to a Monday X post from Alex Thorn, the firm's head of research. The Bitcoin was worth $114.7 million when it was taken, while Thorn put its current value at about $138.8 million.
📊 updated numbers on coldcard exploit
8865 addresses lost 1789.28 BTC worth $114.7m at the time of theft ($138.8m today)
-- loss by address
median 0.00152
mean 0.20184
dormancy median 3.2yr
dormancy mean 3.6yr
-- loss by victim reports (221)
median 1.04272
mean 3.57792
dormancy... pic.twitter.com/d2R29dYyco --- Alex Thorn (@intangiblecoins) August 24, 2026
Of the total, 1,561 BTC, or 87.3%, has not been spent and remains in collection or holding addresses controlled by the attackers. All Bitcoin tied to the first three identified attack waves has also remained unmoved, giving researchers an onchain record of where a large portion of the stolen funds is being held.
Some funds from later attacks have started moving. Thorn said attackers have used CoinJoin transactions, peel chains and other methods designed to make the movement of Bitcoin harder to follow across addresses.
Most Bitcoin from the Coldcard hack remains traceable
Galaxy's latest figures include both address-level analysis and information submitted directly by victims as researchers continue mapping wallets connected to the exploit.
Across the 8,865 addresses identified by the firm, the median loss was 0.00152 BTC and the average stood at 0.20184 BTC, according to figures shared by Thorn. The affected Bitcoin had also remained dormant for long periods before being stolen, with median address dormancy of 3.2 years and an average of 3.6 years.
Victim reports show heavier losses on an individual basis. Galaxy has received 221 reports covering 790.72 BTC, equivalent to 44.2% of the total Bitcoin attributed to the exploit. The median reported loss was 1.04272 BTC and the average was 3.57792 BTC.
Thorn clarified separately that the median means at least half of the 221 reporting victims lost 1 BTC or more. Bitcoin covered by those reports had remained dormant for a median of 3.25 years before the theft, while the average dormancy period was 2.99 years.
You might also like: Coldcard theft: FBI may know 1,082 BTC attacker
The confirmed tally may not account for every loss linked to the incident. Thorn said that including medium-confidence addresses not yet confirmed would increase the estimate to about 1,824 BTC, worth roughly $140 million at the time of the respective thefts.
Earlier estimates changed as researchers identified additional victim addresses and attack patterns. TRM Labs said on Aug. 5 that the incident had involved several waves beginning July 30 and traced the thefts to a firmware problem that weakened the randomness used when generating some Coldcard wallet seeds.
According to TRM Labs, a build configuration error introduced through firmware in March 2021 caused affected devices to fall back on a weaker software random number generator instead of relying fully on hardware-generated entropy. The security firm said the resulting key strength could fall low enough for private keys to be recovered through brute-force computing without physical access to the wallet.
Attackers have started obscuring some later thefts
While the largest holdings remain parked, Galaxy has found different transaction behavior among funds taken during later attacks.
CoinJoin can combine transactions from multiple participants to make it more difficult to connect individual inputs with their eventual outputs. Peel chains involve repeatedly moving smaller amounts from a larger balance into new addresses, creating longer transaction trails for investigators to follow.
Galaxy has continued tracking those movements while sharing identified attacker addresses with cryptocurrency exchanges, compliance companies and law enforcement. Thorn said the effort could allow centralized platforms to identify and potentially freeze stolen Bitcoin if attackers eventually send funds into services where accounts or transactions can be intercepted.
The lack of movement across the first three waves is particularly important to the tracing effort because the corresponding Bitcoin has not yet passed through the obfuscation techniques observed in later activity. Researchers can therefore continue monitoring known addresses for outgoing transactions.
Earlier in August, TRM Labs also reported that most stolen funds were pooling in a limited number of attacker-controlled addresses with little onward movement at the time. Differences between transaction structures across the attack waves led the company to say multiple attackers could have been involved, although it did not attribute the exploit to any specific actor.
Coldcard security had focused on offline key storage
The incident has put attention on a hardware wallet brand built specifically around Bitcoin self-custody.
In May, crypto.news previously reported that Coinkite had released the Coldcard MK5, its first hardware revision to the flagship MK line since the MK4 arrived in 2022. The device retained a dual secure-element design using components from two chip manufacturers and continued supporting air-gapped transaction workflows.
The MK5 also introduced a larger Gorilla Glass display, redesigned physical buttons and improved NFC functionality. Coinkite said at the time that the device continued using open-source firmware while keeping its Bitcoin-only design.
Wallet security had already faced increased attention before the Coldcard losses surfaced. In July, Coinspect disclosed a weakness it called "Ill Bloom," which involved poor randomness during recovery-phrase generation across several software wallets. The security company said about $5 million had moved from exposed wallets by early July, although hardware wallets appeared unaffected by that particular issue.
Weak randomness can become especially dangerous in cryptocurrency wallets because seed phrases ultimately determine the private keys controlling the assets. If the random input used to create a seed contains too little entropy, an attacker with enough computing resources may be able to search the reduced range of possible combinations.
-- Price
Hardware wallet risks have drawn fresh scrutiny
Other wallet security incidents this summer have involved different attack methods.
Ledger's Donjon researchers in July demonstrated a laser attack against a Tangem wallet card that could reset its password and potentially allow transactions to be signed. Tangem said the method required physical possession of the card, specialist knowledge and laboratory equipment costing around $250,000, making the attack different from a remotely exploitable wallet weakness.
Onchain investigator ZachXBT had also criticized hardware wallets in July, saying he did not consider existing devices suitable for signing critical transactions or holding large amounts of cryptocurrency. His comments represented a personal assessment and were not tied to evidence of a new hardware compromise at the time.
The Coldcard incident involves a different failure point because researchers linked the thefts to seed generation on affected devices. TRM Labs said installing updated firmware does not repair a seed that was originally created with weak randomness, meaning users with affected wallets would need to generate a new seed on secure hardware and transfer their Bitcoin to addresses derived from it.
For investigators, the stolen Bitcoin itself remains the main source of evidence. Galaxy has continued distributing confirmed attacker addresses to exchanges, compliance firms and law enforcement while monitoring the 1,561 BTC that has yet to leave attacker-controlled collection and holding wallets.
Read more: Monad proposes wallet upgrade for passkeys, recovery and quantum security
This content is provided for general informational purposes only and doesn't constitute financial, investment, legal, or tax advice. Any events, rewards, online promotions, or related information mentioned herein should not be considered a recommendation, solicitation, or invitation to purchase, sell, trade, or otherwise deal in any crypto assets. Crypto assets are highly volatile and may result in loss. The availability of WEEX services, products, and related events may vary by region. You are responsible for ensuring that your participation is in accordance with applicable local laws and regulations.
You may also like
Citi says 77% of institutions eye tokenized collateral
FTX and AI Apocalypse: The End of Calm Times for Anthropic
What is CBDC? Governments Push for Development of Central Bank Digital Currencies
Bitcoin Has Not Fallen Below Realized Price During the Bear Market
The Clearing House Selects Quant for US Tokenized Deposit Network
4500 Bitcoins Moved to New Addresses, Sale Status Unconfirmed
[New York Gold, Bonds, Dollar] Interest Rates and Dollar Strength Pause... Oil Prices Drop, Won and Gold Prices Rebound
Trump Expresses Concern Over Yen Depreciation, Japanese Finance Minister Says Coordination with U.S. Will Continue
Treasuries at 21-Year High: Impact on Stocks and Interest Rates
Solana DEX volume spike hides circular trades, and automated bots are blamed
Oracle Stock vs. KRAFTON Stock: Why Are Investors Questioning Two Growing Companies?
Compare Oracle and KRAFTON stocks through their latest results, share-price questions and the different growth tests investors face in 2026.
John Templeton: "Bull markets are born in pessimism"
The Death of Hsin-Ju: A Prelude to Conspiracy
LTC Airdrop 2026: How to Claim 50,000 USDT Rewards on WEEX
Raiffeisen’s crypto deal could reach 18 million customers. How many can actually trade?
TRON Surpasses $30T in Total Transaction Volume as it Secures its Place as Leading Chain for Stablecoins
HTX DeepThink: Opportunities Concentrate on Profitable and Fund-Supported Assets, BTC Still Has Room for Recovery After Consolidation
Why Did Sui (SUI) Crypto Price Jump 44%? Crypto OI and Leverage Explain the Rally
See why Sui (SUI) jumped 44%, how crypto OI and leverage amplified the rally, what the pullback means, and how to trade SUI on WEEX.
Circle expands CCTP to EURC and cirBTC on Arc
Bitcoin, Sports, and Politics: Predictive Markets Target $10 Trillion
AI Agent Jev Expects On-Chain Innovation Through Automated Judgment
The End of the Blank Prompt: Why Trading AI Needs a Playbook
Stablecoins hold nearly $200 billion in US debt, but money funds bought the surge
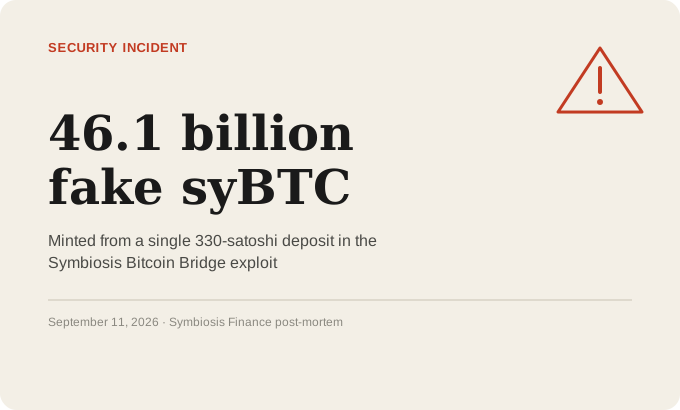
How Did a Hacker Create 46 Billion Fake Bitcoin in the Symbiosis Exploit? Decodes Bitcoin Hacker With WEEX Now
How two Symbiosis bridge bugs let a hacker mint 46.1 billion unbacked syBTC, drain Bitcoin pools and expose critical bridge risks.
CFTC's Selig Emphasizes the Need to Prepare for the Era of Large-Scale Tokenization in the U.S.
The IMF opens an office in Venezuela to supervise an economy that has already migrated to USDT
SOXL Stock Jumped 12% Yesterday: Three Companies Explain the Entire Move
Bitcoin's Hashrate Rises as Miners Reactivate Their Machines
Bitcoin 2x Leveraged ETF Launches on Cboe, But Doesn't Buy Bitcoin: Here's Why
Crypto: The ECB Enters the Tokenized Bond Market
Citi says 77% of institutions eye tokenized collateral
FTX and AI Apocalypse: The End of Calm Times for Anthropic
What is CBDC? Governments Push for Development of Central Bank Digital Currencies
Bitcoin Has Not Fallen Below Realized Price During the Bear Market
The Clearing House Selects Quant for US Tokenized Deposit Network
4500 Bitcoins Moved to New Addresses, Sale Status Unconfirmed





